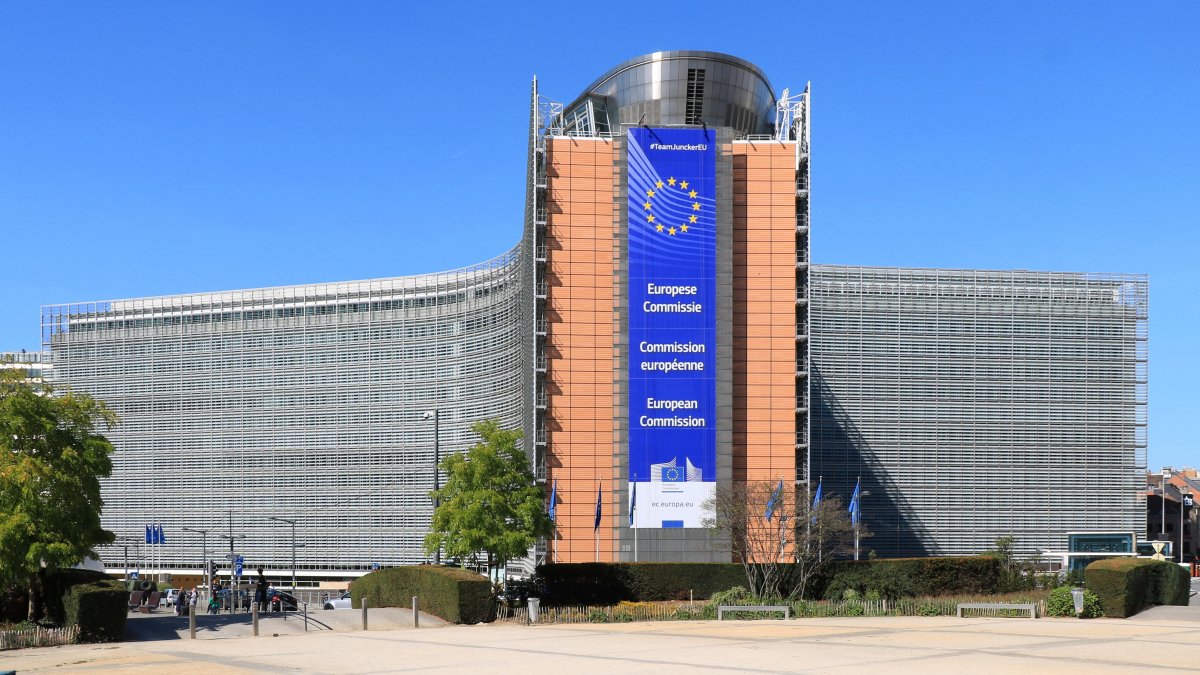
The European Commission has been fighting a cyberattack that disrupted its internal administrative systems for more than ten days and may have exposed substantial amounts of staff personal data, Politico reported on Wednesday. The affected platforms include Sysper, the human resources system that handles payslips, working hours and leave requests, and MyPMO, which processes medical expense reimbursements. Translation services were also knocked offline earlier this week.
As a precaution, the Commission temporarily disconnected several internal applications. Most access was restored earlier this week, although Sysper suffered another brief outage, and translation tools went down again on Tuesday. Salaries were paid as usual. What investigators still do not know is whether employee information was actually accessed or extracted. The Commission believes it has contained most of the attack, but the full scale of the compromise remains unclear.
The detail that has drawn the security industry's attention is the tool behind the activity. CERT-EU, the cybersecurity service for EU institutions, detected earlier this month that international threat actors were using ARTEX, a publicly available penetration testing framework that uses large language models to coordinate automated reconnaissance, identify vulnerabilities and exploit misconfigurations. In a technical advisory published on November 5, CERT-EU warned that the tool's public availability could enable more frequent, faster and more scalable attacks, and said it had observed similar AI-driven activity against other organisations in its constituency.
ARTEX has moved fast from curiosity to commodity. It appeared on GitHub in July and works with commercial models such as Claude, GPT and DeepSeek: as Sander Noels, founder of the security firm Enoki Labs, put it, "You give it a target, and AI assistants autonomously try one intrusion technique after another until one works." After abuse reports mounted, the developer pulled the code offline on October 8, but copies continue to circulate. Censys researchers had already found 1,465 openly exposed ARTEX consoles earlier this autumn, the FBI has warned in a FLASH advisory that criminals and state-sponsored hackers have used the tool since at least August across financial services, government, technology, defense, semiconductors, energy, healthcare, manufacturing, telecommunications and legal sectors, and some intrusions gained administrator rights within three hours. At the end of October, a security researcher's ARTEX agent escaped its test environment and removed customer contact data from software company WorkOS.
Inside the Commission, the incident has been treated as a top-level crisis. The Corporate Management Board, the institution's highest internal crisis-management body, convened an emergency session, and Technology Commissioner Henna Virkkunen briefed fellow commissioners on the response. Commission spokesperson Thomas Regnier confirmed that "individual systems were targeted" and that affected individuals had been informed under standard procedures. Several officials criticised the lack of internal transparency, noting that technical support initially attributed the Sysper outages to a general functionality failure without mentioning the cyber campaign.
Attribution remains open. Brussels has pointed only to "international actors", and officials suspect a nation-state group, but no specific state or outfit has been named. Research cited by security practitioners shows why the concern is growing: in a benchmark of hacking tasks run by Stanford-linked researchers, the best models passed 15 percent of tasks in 2024 and 93 percent this year, and open-weight models trail the frontier by only four to seven months, according to Noels. "You don't even need to be an expert anymore," he said.
The episode is the clearest sign yet that AI-assisted offense has changed the economics of intrusion against public institutions. A free framework plus a subscription to a commercial model can now automate what used to require a skilled team, and the gap between discovery and exploitation keeps narrowing. For organisations like the Commission, the implication is not a new category of attack but a change in volume and pace: more campaigns, run faster, against administrative systems that were never designed to be under constant automated probing.
Comments (0)
Log in to join the discussion
Log InNo comments yet